Memory-safe, lightweight Linux-compatible userspace kernel to safely sandbox agents at high density without virtual machine overhead.
Handle bursty code execution demand with high density from agentic tools, distributed RL environments, LLM-generated code, autoresearch and data science exploration.
Pack orders of magnitude more sandboxes per node by reclaiming idle memory dynamically back to the host. Eliminate hypervisor boot phases and memory fragmentation.
Deliver container-native pod density, instant cold starts, and dynamic host memory allocation without requiring nested virtualization inside virtual machines.
Standard containers lack isolation and microVMs still carry high idle memory and slow initialization overhead when compared to native containers.
Harden clusters like Kubernetes against container breakouts, shared-kernel vulnerabilities, and unpatched host kernel CVEs.
Sandbox workloads by inserting an independent user-space kernel, removing direct access to the host Linux kernel.
Run agents and AI workloads without fragmenting Kubernetes tooling or pod specs.
gVisor implements the OCI Runtime Spec, functioning as a standard Kubernetes RuntimeClass without requiring custom VM images or hypervisor network bridges.
Automatically checkpoint idle sandboxes and seamlessly resume them in milliseconds via integration with Agent Substrate.
gVisor natively integrates with Agent Substrate in Kubernetes, yielding superior density and checkpoint/restore performance.
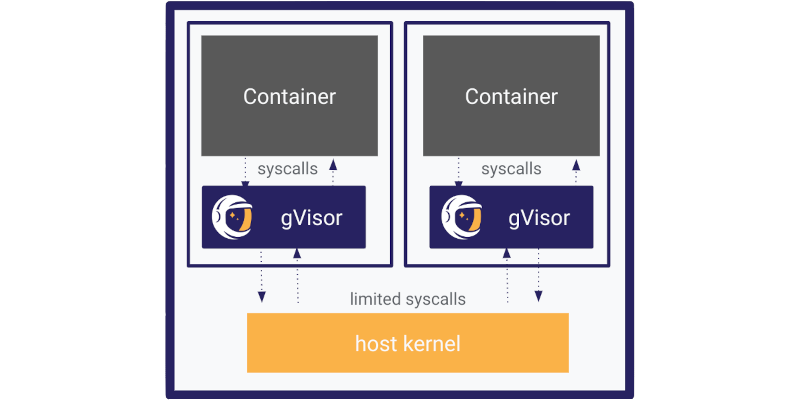
gVisor implements core Linux kernel abstractions (process management, memory layout, network stack, VFS) so that application syscalls are serviced in user space, isolating the host kernel from guest code.
gVisor allocates and releases host OS memory natively as a container does, rather than using guest OS ballooning drivers. This eliminates memory fragmentation issues and enables packing more sandboxes per host.
Bypass virtual hardware initialization sequences (virtual BIOS, vCPU configuration, PCI bus enumeration, guest kernel boot). Launch isolated sandboxes with process-like startup latency, ideal for high-throughput tool calling and short-lived execution tasks.
gVisor supports GPU and TPU accelerators. Driver operations are relayed to the host kernel drivers, with near-native performance and zero memory copying overhead.
NVIDIA GPU workloads may be seamlessly checkpointed and restored within gVisor. GPU memory pages are streamed in from checkpoint storage as they are restored into VRAM, with hardware speeds as the only bottleneck.
Attach probes and trace sessions to gVisor sandboxes, providing real-time observability over sandbox events.
gVisor implements the Linux API: by intercepting all sandboxed application system calls to the kernel, it protects the host from the application. In addition, gVisor also sandboxes itself from the host using Linux's isolation capabilities. Through these layers of defense, gVisor achieves true defense-in-depth while still providing VM-like performance and container-like resource efficiency.
gVisor runs with the least amount of privileges and the strictest possible system call filter needed to function. gVisor implements the Linux kernel and its network stack using Go, a memory-safe and type-safe language.
gVisor runs anywhere Linux does. It works on x86 and ARM, on VMs or bare-metal, and does not require virtualization support. gVisor works well on all popular cloud providers.
gVisor works with Docker, Kubernetes, and containerd. Many popular applications and images are deployed in production environments on gVisor.
gVisor containers start up in milliseconds and have minimal resource overhead. They act like, feel like, and actually are containers, not VMs. Their resource consumption can scale up and down at runtime, enabling container-native resource efficiency.
gVisor can checkpoint and restore containers. Use it to cache warmed-up services, resume workloads on other machines, snapshot execution, save state for forensics, or branch interactive REPL sessions.
Observe runtime behavior of your applications by streaming application actions (trace points) to an external threat detection engine like Wiz and generate alerts.
gVisor applications can use TPUs and CUDA on Nvidia GPUs, bringing isolation to AI/ML workloads.