Blog
FeedThe anatomy of a 3B step
This article was contributed by Tines. Shayon Mukherjee is an engineer at Tines, working on the runtime infrastructure behind 3B. It was originally published on Tines Notebook.
At Tines we’re building 3B, where people work with an agent to automate enterprise software. Workflows, internal apps, and agents are all made of steps, each a directory with a Dockerfile and a program that reads stdin and writes stdout. The result becomes the input to whatever runs next.
Each run gets a fresh Linux sandbox, including a fresh gVisor application kernel, which we delete afterwards because we have to treat the program as untrusted even if it appears to have worked. That means its image and persistent files have to survive outside the environment we throw away.
Blink and it's back: how gVisor checkpoint/restore got 5x faster
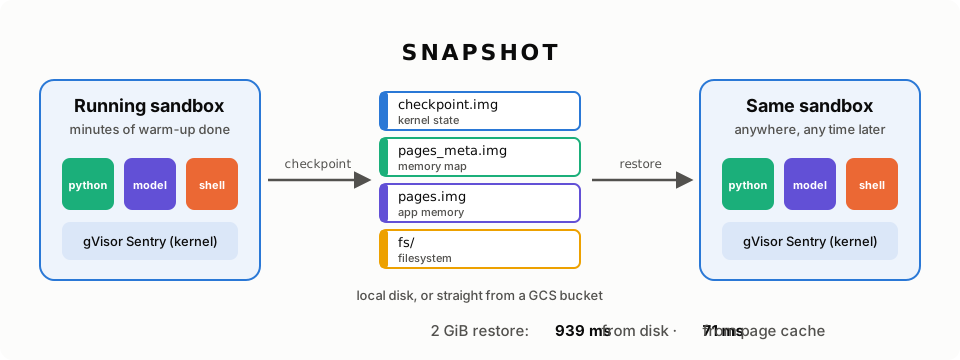
runsc checkpoint saves the full state of a gVisor sandbox to files: every
process, every open file, every socket, and the application’s memory.
runsc restore brings it back, on the same machine or on a different one, and
the applications continue as if nothing happened.
This feature is not new. gVisor could checkpoint a sandbox in 2018. But the 2018 version was slow, and some people still think of gVisor checkpoint/restore that way. A lot changed in the last few years. In our tests below, restoring a 2 GiB sandbox from a slow disk went from 5,106 ms to 939 ms, about 5 times faster, saturating the max speed of the disk. When the image is already in the host page cache, it went from 651 ms to 71 ms.
gVisor is being donated to CNCF
In 2018, Google open-sourced gVisor under the Apache 2.0 license. To the best of its contributors’ knowledge, it has ever since remained the second most mature implementation of Linux, after Linux.
This year, the gVisor project is being donated to CNCF, and its governance model is shifting accordingly.
Who needs VMs? Run systemd and full Linux desktop apps in gVisor
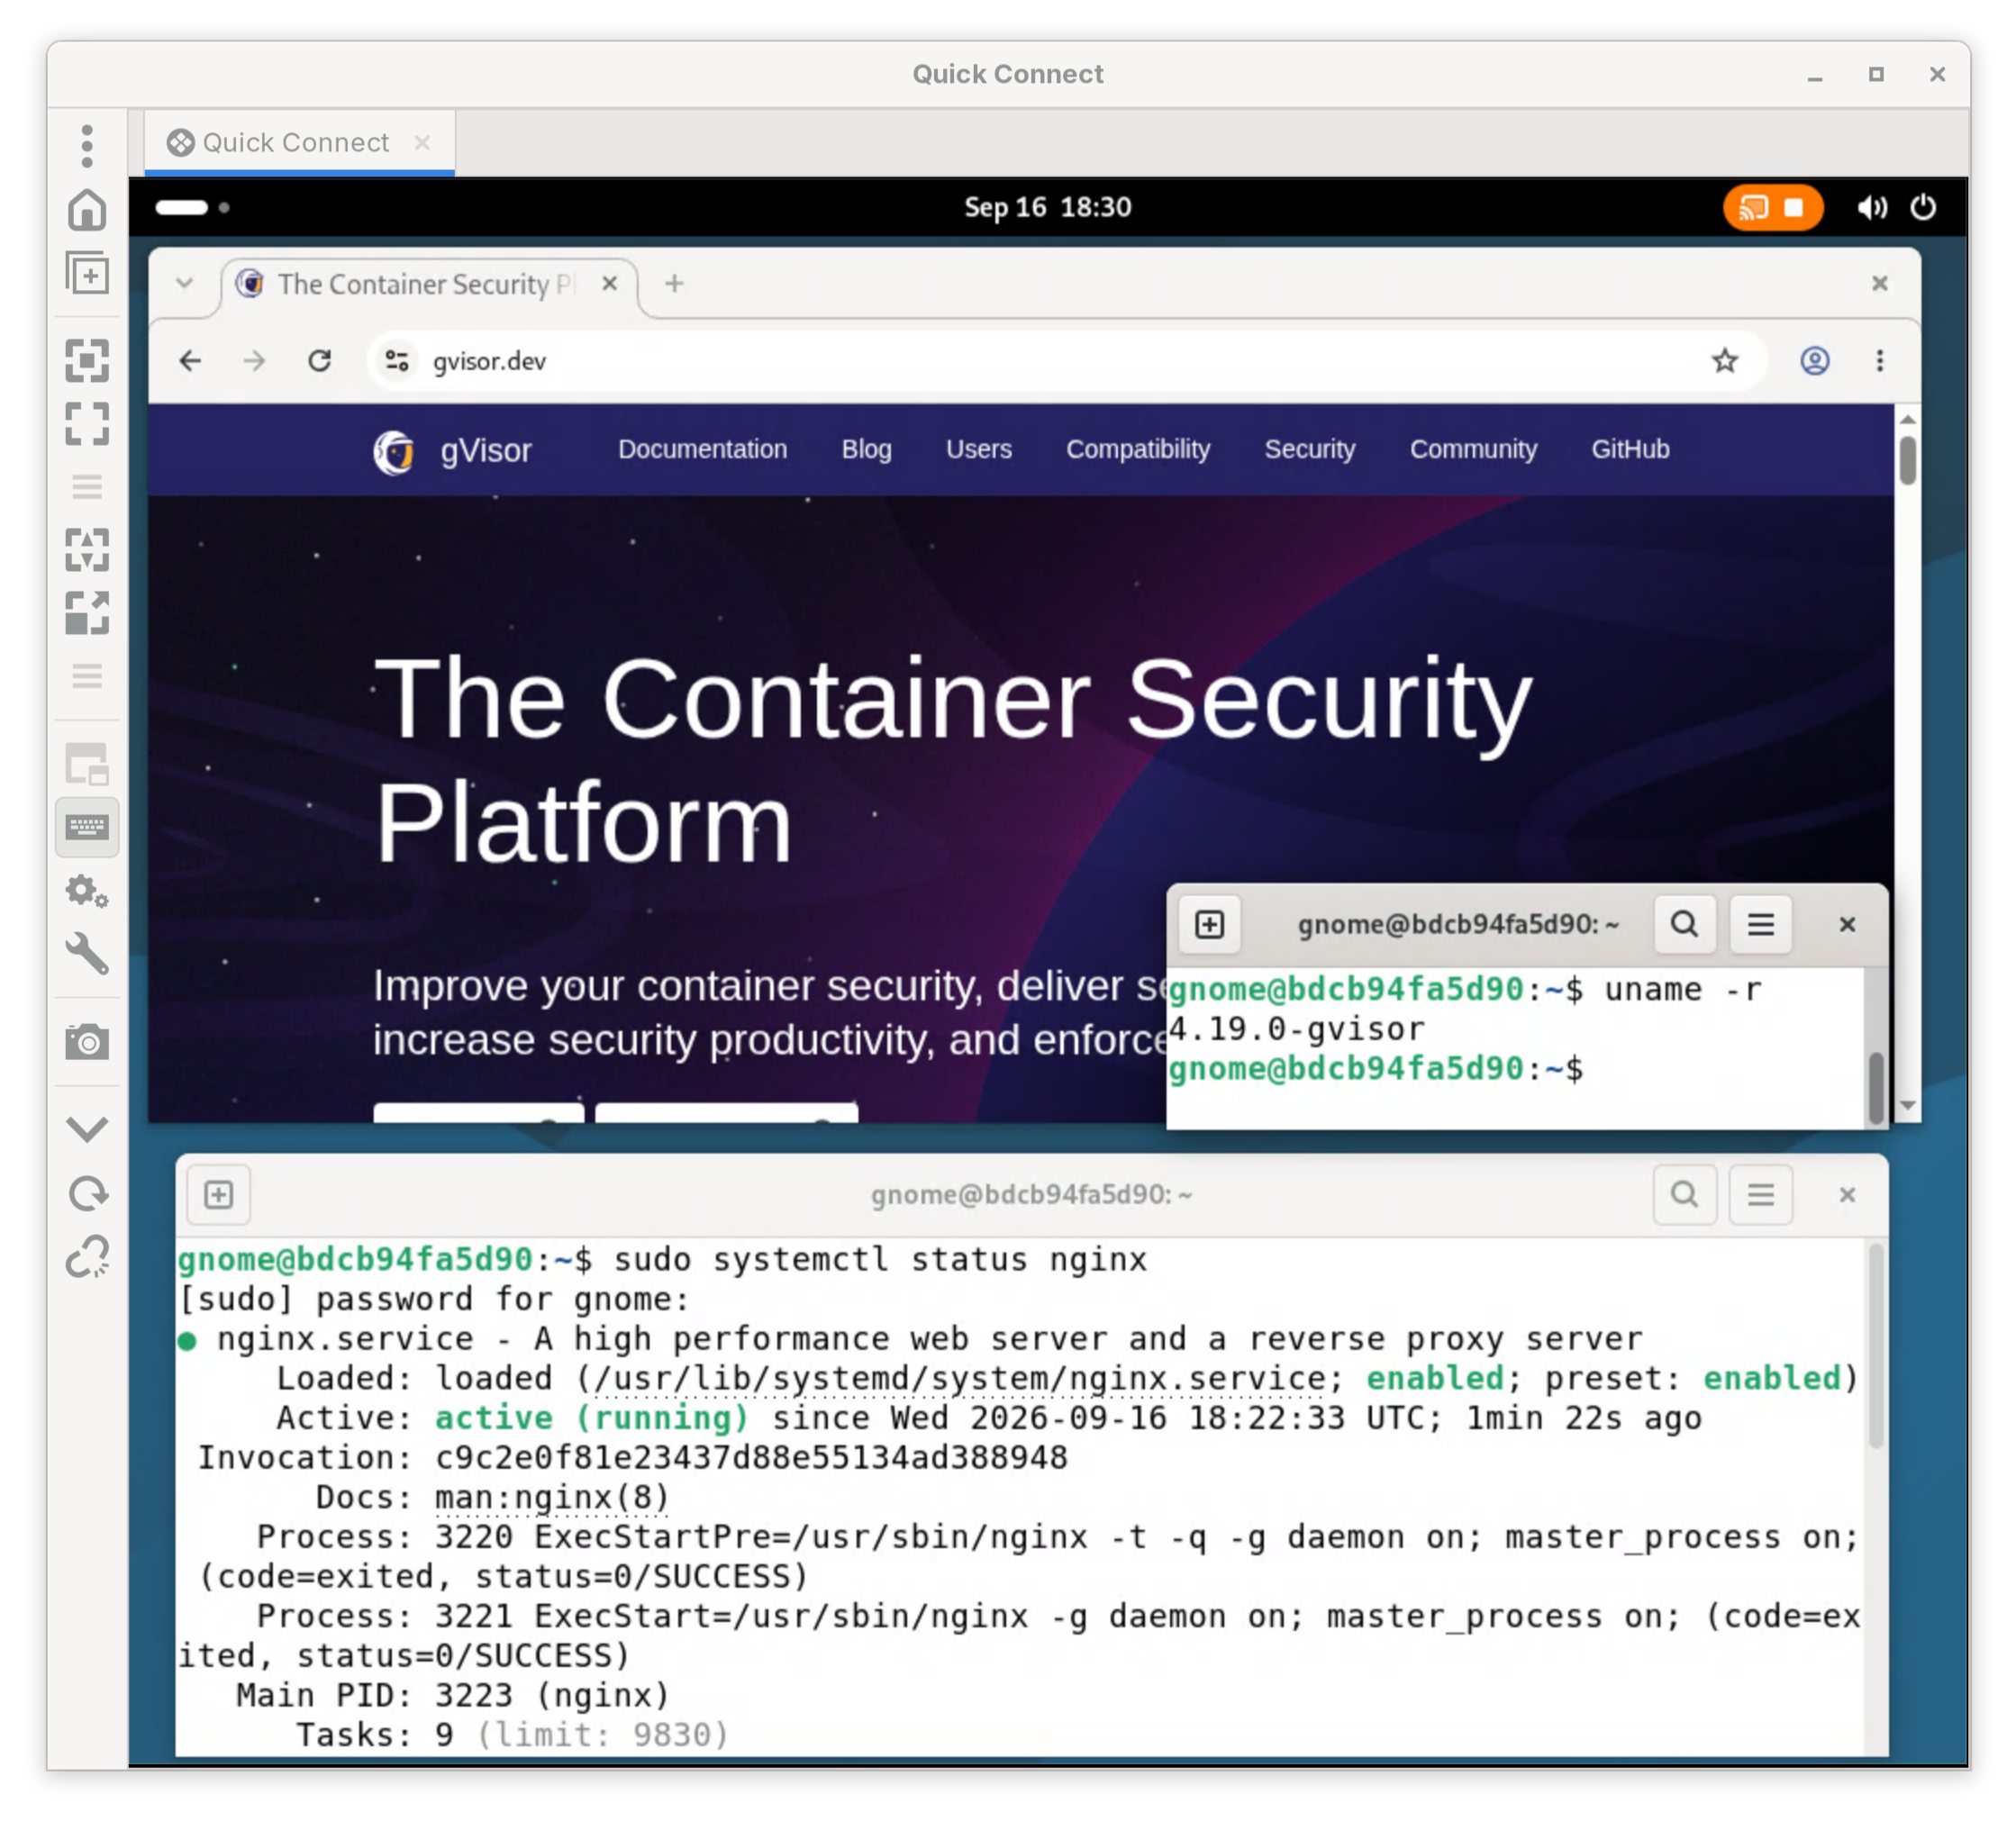
As an OCI runtime, gVisor is traditionally used to sandbox application containers containing a single service. These containers have little to no userspace running in them except the service itself. While this is great for efficiency and scalability, there are some use cases that can benefit from having something closer to a full Linux system inside the sandbox, with a “normal” service manager and system daemons.
gVisor now has gained support for running systemd. To this end, support for a handful of major new kernel APIs has been added to gVisor, including:
- The new mount API,
- Cgroups v2,
- Pidfds,
- POSIX ACL support for
tmpfsandoverlayfs, - The
openat2(2)system call,
along with numerous smaller features and bug fixes.
Systemd has been tested to work in full-system gVisor containers with Ubuntu, Debian, and Red Hat’s Universal Base Images.
Scaling Agentic-RL Sandboxes to the Millions with gVisor at Tencent
This article was contributed by Tencent. Yifeng Tan, Hua Liu, and Hui Chen are engineers at Tencent, responsible for the internal container infrastructure.
As LLMs evolve from chat interfaces to autonomous agents, building a robust and
secure isolation environment becomes a necessity. We chose
gVisor as the default sandbox for our Agentic-RL
scenarios. Today, we run millions of gVisor sandboxes daily for Agentic-RL
training in production, and that scale continues to grow. After more than
74,000 side-by-side comparisons between runsc (gVisor) and runc
(unsandboxed/Linux), combined with targeted fixes driven by real-world
workloads, we have essentially closed the execution correctness gap with runc,
fully meeting our production-grade business requirements. During this process,
we successfully investigated and resolved gVisor compatibility issues that
accounted for approximately 1.7% of all test cases.
This post focuses on CPU-centric code execution and testing workloads. We will discuss gVisor compatibility verification and highlight representative issues, skipping implementation details like GPU support, image distribution, or cluster scheduling. We aim to answer three questions:
- Why choose gVisor?
- Why doesn’t manual compatibility verification scale?
- How can AI agents analyze compatibility issues, what do typical failures look like, and what best practices have we established?
If you would like to contribute to the gVisor blog check out the instructions.